Skip to content
Modern IT is quickly incorporating artificial intelligence. Businesses use AI for customer relationship management, automation, data analysis, content generation, cybersecurity, and decision-making.
However, as AI evolves and integrates with business processes, companies require precise answers to a crucial question: what information can the system access? What choices is it able to make? How should you monitor its security and performance? Who has accountability for its deeds?
AI governance becomes crucial in this situation.
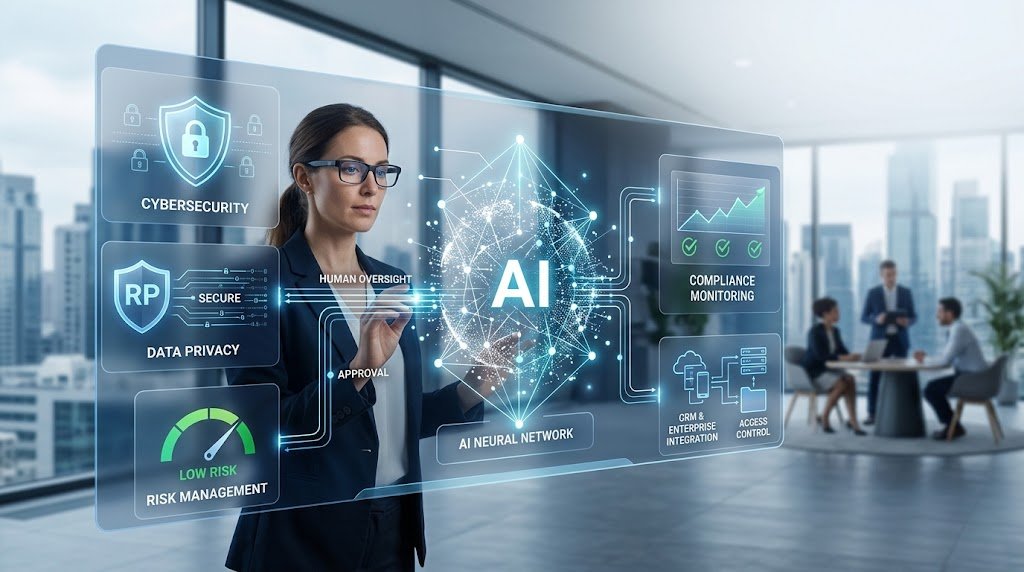
I view AI Governance as a crucial component of IT strategy, not only a legal or compliance function, based on my expertise with AI automation projects, data protection, CRM and enterprise systems, risk management, compliance, cybersecurity, responsible AI, and client implementations.
Its objective is to assist businesses in using AI in a responsible, safe, secure, and long-lasting manner.
What Is AI Governance?
AI governance refers to the system an organization employs to handle the selection, development, deployment, access, monitoring, and use of artificial intelligence.
Typically, a practical framework includes:
- AI guidelines and appropriate usage
- Privacy and data access
- Cybersecurity
- Risk evaluation
- Approval of the model and application
- Human supervision
- Observation and auditing
- Adherence to regulations
- AI tools from third parties
- Documentation and accountability
Stopping the adoption of artificial intelligence technology is not the aim. It is to set up suitable controls so businesses may profit from AI without taking needless risks.
Why AI Governance Matters in IT
CRM platforms, databases, cloud applications, APIs, internal documents, communication systems, and other enterprise technologies are becoming increasingly connected to AI systems.
Although this connectedness adds a lot of value, it also makes errors more likely to have an impact.
Excessive permissions could give an AI system access to data it doesn’t require. Using an unapproved AI platform, an employee can inadvertently reveal private information. Without enough human scrutiny, an automatic system could decide.
Thus, IT teams need to comprehend:
- Which AI systems are in use?
- What information are they able to access?
- Who can make use of them?
- What can they do?
- Which decisions require human approval?
- How the system tracks their actions
- Who is accountable for the results?
These are not just legal inquiries. These are basic questions on data, operations, security, and IT.
AI Governance Is More Than Compliance
The idea that AI governance is largely a legal or compliance issue is one of the most frequent errors I have come across.
While compliance is crucial, governance goes beyond that.
Technology, data, risk management, cybersecurity, business procedures, and human accountability are all connected.
Organizations may overlook real-world dangers—including excessive permissions, poor data quality, unauthorized AI use, improper monitoring, and insecure integrations—if they view governance primarily as paperwork or a compliance checklist.
The design and operation of AI systems should incorporate effective governance.
Key Components of AI Governance
AI Policies and Acceptable Use
Clear policies must guide organizations on permitted AI tools, employee usage limits, and safe data inputs.
Policies must cover both permitted AI systems and the unlawful use of third-party platforms.
Data Privacy and Access Control
Systems should only be able to access the data they require.
Organizations must properly control sensitive data, including customer information, employee records, financial details, intellectual property, internal papers, and credentials.
For automated systems and AI agents in particular, the least privilege concept is crucial.
AI Security
Additional cybersecurity issues brought forward by AI include:
- Immediate injection
- Unauthorized entry
- Exposure of confidential data
- Overuse of permissions
- Input manipulation
- Integrations that are vulnerable
- Compromised credentials
- Automated activities that are unsafe
Therefore, organizations must integrate security measures from the start of AI system development.
Risk Assessment and Model Approval
An AI system used to make important business decisions is far different from a tool for coming up with marketing concepts.
Organizations should evaluate AI use cases using criteria like
The degree of danger associated with each AI application varies.
- Sensitivity of data
- Degree of independence
- Possible consequences of mistakes
- connected system
- The number of individuals impacted
- Exposure to security
- Requirements for regulations
Applications that pose a greater risk have to be subject to more stringent evaluation, approval, and oversight.
Human Oversight and Accountability
AI shouldn’t be used as an excuse to eliminate human accountability.
In high-risk applications, humans should be able to assess outcomes, approve crucial decisions, intervene when necessary, and assign blame when anything goes wrong.
Depending on the use case, companies may need:
- Consent from people for dangerous decisions
- Analysis of data generated by AI
- Continuous observation
- Clearly stated responsibility and ownership
- Audit trails
Eliminating automation is not the goal. It is to guarantee that automation functions within suitable bounds.
AI Automation Should Include AI Governance
My experience with AI automation and CRM systems suggests that governance shouldn’t be a post-implementation bureaucratic layer.
Teams must incorporate it straight into the process.
For example, an automated CRM process could look like this:
- Acquisition of leads
- Validation of data
- Verification of permissions
- AI processing
- Automated action
- When necessary, human approval
- Observing and recording
- Evaluation of performance
With this strategy, companies can automate procedures while keeping the proper level of management.
Data Quality Is Part of AI Governance
Poor data can compromise even a highly developed AI implementation.
Poor business decisions and unreliable AI outputs might result from outdated, redundant, incomplete, or erroneous information.
Because of this, data quality is crucial to the responsible application of AI.
Organizations ought to concentrate on:
- Validation of data
- Data purification
- Preventing duplication
- Classification of data
- Management of access
- Monitoring of data quality
A solid data foundation is necessary for effective AI governance.
The Growing Risk of Autonomous AI
The governance dilemma is evolving thanks to generative AI and AI agents.
Conventional automation often adheres to predetermined guidelines. AI agents are becoming more proficient in making recommendations, interpreting data, interacting with systems, and acting independently.
As a result, organizations require precise boundaries regarding:
- The capabilities AI agent
- Which systems are accessible to them?
- What data it can utilize?
- Which activities require approval?
- How to deal with strange behavior?
- How to record activities?
- How to restrict an access?
Appropriate controls become increasingly crucial as autonomy increases
Exposure of Private Information and Third-Party AI
Workers are using AI more often for writing, research, analysis, summarization, coding, and other jobs.
Organizations must understand what happens to business information when it joins an external AI service, even while the convenience is clear.
Before authorizing third-party AI solutions, companies ought to think about:
- What information does the system process?
- How does the system gain access?
- Where does the system store data?
- Which security measures are in place?
- Which integrations are active?
- Which contractual safeguards are applicable?
- How are incidents managed?
Corporations must control AI adoption rather than leaving it solely to staff members.
Ongoing Observation and Auditing
AI governance continues once an AI system is authorized.
Organizations should pay attention to crucial systems for:
- Performance and accuracy
- Unexpected outcomes
- Events about security
- Access patterns
- Policy infractions
- Utilizing data
- Changes made to the system or model
With the help of proper documentation and audit trails, organizations can better understand how workers use AI and investigate problems when they occur.
AI Governance in Small Enterprises
It is not just a business issue.
Small and expanding companies use AI for operations, marketing, sales, customer support, CRM automation, and content production.
They nevertheless require real control even if they don’t require a sizable governance staff.
Businesses should, at the very least, create explicit regulations for the use of AI, safeguard confidential information, restrict access, keep an eye on critical systems, and specify when human permission is necessary.
Creating governance that is commensurate to risk rather than unduly complex is crucial.
Common AI Governance Mistakes
Practically speaking, companies should steer clear of the following typical errors:
- Using AI before establishing governance guidelines
- Disregarding the quality of data
- Giving AI too much access
- Using high-risk AI without human supervision
- Failing to monitor systems after deployment.
- Considering governance as only a checklist for compliance
- Permitting unrestricted usage of AI tools from third parties
- Not defining accountability
- Making governance so difficult that workers avoid it
Good governance must safeguard the organization while remaining realistic enough for employees to follow.
How IT Leaders Can Approach AI Governance
A sensible place to start is to:
Identify AI Usage
Make a list of all the AI tools, models, agents, and automated processes that are currently in use throughout the company.
Classify Risk
Consider data sensitivity, autonomy, business effect, security exposure, and regulatory constraints while evaluating each use case.
Define Policies and Permissions
Set explicit guidelines for the use of AI, data access, authorized tools, and staff duties.
Build Controls into Workflows
Organizations can directly integrate AI and automation workflows with approval procedures, access controls, monitoring, logging, and security measures.
Establish Human Oversight
Define which AI-generated decisions and actions require human review.
Monitor and Improve
As technology and the business environment evolve, keep an eye on AI performance, security, data usage, and compliance.
Final Thoughts
Organizations cannot afford to regard governance as an afterthought as AI becomes an essential component of modern IT.
Technology, cybersecurity, data management, compliance, risk management, and human accountability are all integrated into effective AI governance.
It assists companies in safeguarding confidential data, lowering risks associated with AI, fostering responsible innovation, enhancing trust, and preventing expensive errors.
The systems where AI functions—AI workflows, CRM platforms, access controls, security procedures, data management, monitoring, and approval processes—should, above all, incorporate governance.
The goal of AI governance is not to slow down AI.
About the Author
Sajid Abbas | Marketing and Sales | AI Automation & CRM Specialist for US B2B | Web Design, Lead Generation
I help US SMBs transform their digital presence through AI automation, CRM optimization, web design, and lead generation. With experience serving businesses across multiple industries, I specialize in turning fragmented digital tools into unified revenue engines.